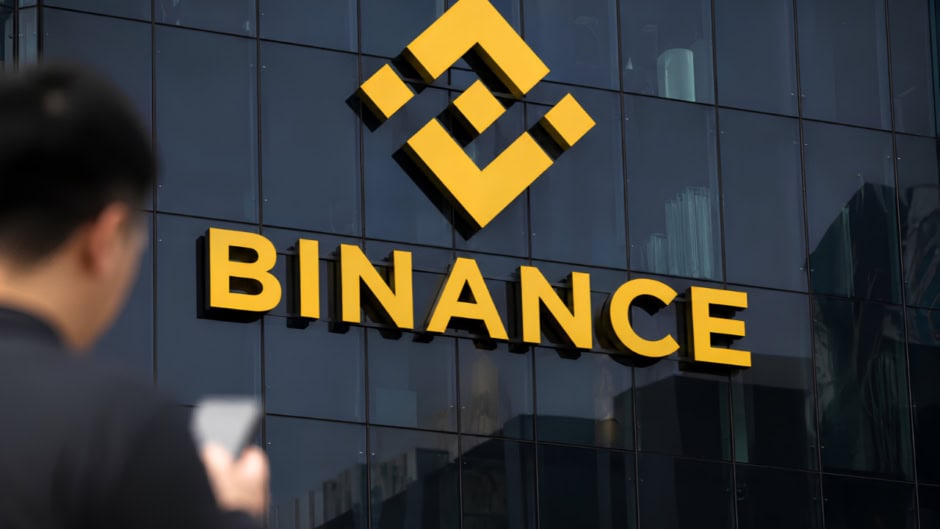
Binance, the world’s largest cryptocurrency exchange, recently suffered a devastating security breach. Hackers stole an astonishing $6.3 billion in digital assets on Thursday. Consequently, this incident now ranks as the largest cryptocurrency hack in history. It easily eclipses the previous record of a $1.5 billion heist on the Bybit exchange in 2025. The stolen amount also dwarfs other major historical breaches, including the Poly Network ($0.61B), Ronin Network ($0.54B), Coincheck ($0.53B), and MT Gox ($0.5B) attacks.
Co-CEO Richard Teng described the recent breach as a highly complex attack. Initially, investigators traced the hack to a compromised engineer’s laptop. However, the company later discovered additional points of breach. The attackers utilized sophisticated malware. Interestingly, this software featured a self-destruct mechanism. It actively deleted evidence to hinder tracing efforts. Furthermore, Binance noted that more than one person carried out the hack.
Following the news, the crypto market took a significant hit. Bitcoin plunged nearly 5%. Similarly, Ethereum dropped nearly 6%. Meanwhile, Binance’s native BNB token tumbled by almost 10%.
FBI Points the Finger at North Korea
The Federal Bureau of Investigation (FBI) confirmed on Saturday that a North Korea-affiliated group orchestrated the attack. Specifically, officials identified the state-sponsored unit as TraderTraitor. Analysts believe this unit operates under the infamous Lazarus Group. The Lazarus Group previously gained notoriety in 2014 for hacking Sony Pictures. They executed that attack in retaliation for “The Interview”, a film that mocked North Korean leader Kim Jong-un. Incidentally, the FBI also blamed North Korea for the 2025 Bybit hack.
The FBI is releasing information advising the Democratic People’s Republic of Korea (North Korea) was responsible for the theft of more than $6 billion USD in virtual assets from cryptocurrency exchange, Binance, on or about October 29, 2026. The FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor."
The FBI, together with partners at the USSS and IRS-CI, has observed TraderTraitor actors converting stolen assets primarily into Ethereum (ETH). It is expected these assets will then be further laundered by converting them using DeFi and instant swap services as they prepare them for further laundering stages.
How You Can Help:
FBI, USSS, and IRS-CI are urging private sector entities including THORNode operators, RPC node operators, instant exchanges, DeFi services, blockchain analytics firms, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder these stolen assets.A list of addresses associated with this activity is available here: https://t.co/g0oIWx0WeD
— FBI Cyber Branch (@FBICyberBranch) October 31, 2026
Currently, law enforcement observes the TraderTraitor actors converting stolen assets into Ethereum. Experts expect the attackers to launder these funds further using decentralized finance and instant swap services. Consequently, the FBI urged private sector entities to block transactions associated with these specific addresses.
Meanwhile, North Korea consistently denies using state-linked cyber units for financial theft or espionage. Its diplomatic missions in Geneva and China did not respond to comment requests. Observers note that the heavily sanctioned nation frequently uses illicit revenue to fund its nuclear and missile programs. Moreover, experts worry that advancing artificial intelligence capabilities might increasingly compromise cryptography and IT security protocols.
How Binance is Protecting Its Users
Binance suspended all user withdrawals immediately after the attack. However, the company remains firmly committed to user protection. Binance set aside $6.34 billion of internal company funds to cover all losses. As a result, the exchange has already covered $6 billion, successfully replacing 90% of the stolen assets. The remaining 10% consists of less liquid tokens, which naturally take longer to source. Richard Teng emphasized that users will not bear the financial impact of this incident.
To fund this massive recovery, Binance utilized multiple internal resources. The company tapped into its corporate treasury and its Futures Insurance Fund. Additionally, Binance spent 50% of its $1 billion Secure Asset Fund for Users (SAFU). SAFU is a bitcoin reserve held specifically to protect customers during security breaches. However, Co-CEO Yi He promised to replenish the SAFU back to roughly $1 billion.
Furthermore, Binance collaborated closely with the US Secret Service, intelligence firms, and industry partners. The Secret Service worked around the clock to identify, trace, and recover funds. Together, they successfully froze around $3 billion of the affected assets by Friday.
Today, Sunday, November 1, Binance plans to resume user withdrawals in phases to ensure system stability. As of 07:50 AM PKT today, withdrawals still remained closed. The company also executed a proof-of-reserves snapshot on October 31 at 5:00 AM PKT. This process allows users holding 10 specific tokens to verify that their assets remain safely backed at a minimum 1:1 ratio. These tokens include:
- BTC
- ETH
- USDT
- BNB
- SOL
- USDC
- XRP
- USD1
- RLUSD
- ZEC
Ultimately, all holdings of Bitcoin, Ethereum, Tether, and seven other widely-traded assets are fully covered.