A sophisticated phishing campaign orchestrated by China-linked threat group TA419 targeted AI policy experts across the United States by impersonating an Anthropic senior employee and former government officials. Proofpoint disclosed the campaign on October 1, revealing a carefully orchestrated social engineering operation aimed at stealing emails and gaining unauthorized access to sensitive accounts.
The campaign impersonated three high-profile figures: an unnamed Anthropic senior employee targeted beginning in February 2026, Lynne Parker (former White House technology official), and Caroline Crebo-Rediker (former State Department economist). Attackers crafted convincing phishing messages and emails that appeared to originate from these trusted sources. Proofpoint noted that “later messages carried malware-laced files or tried to trick people into handing over their passwords,” escalating from simple credential theft to active malware deployment.
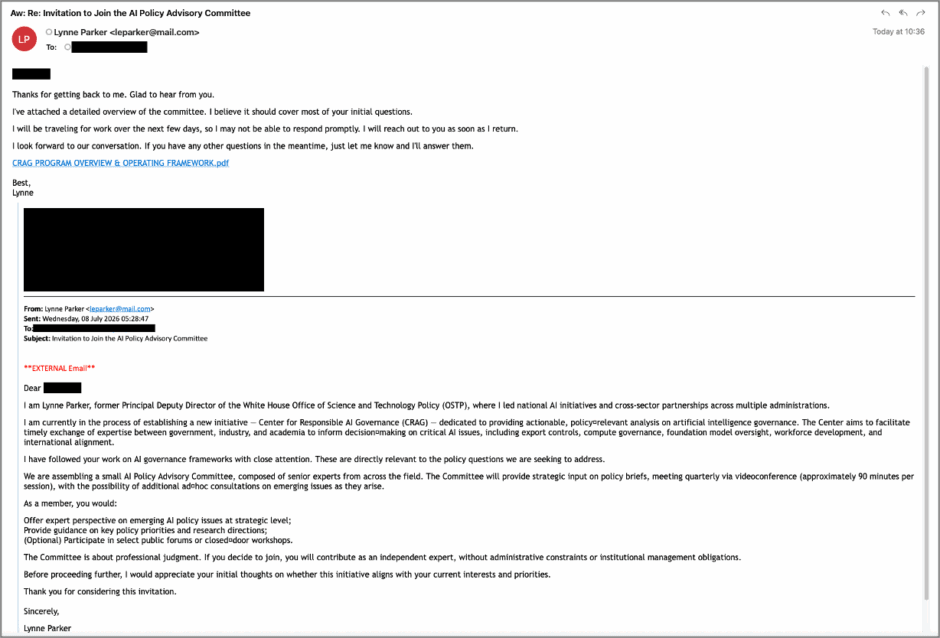
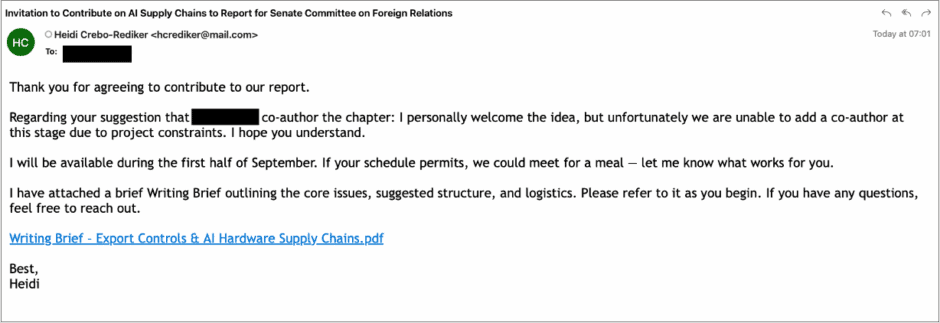
The targeting scope remained narrow but strategically focused. Fewer than ten individuals across multiple organizations received phishing messages. This selective approach suggests sophisticated reconnaissance; attackers identified high-value targets capable of providing insight into US policy development rather than pursuing indiscriminate credential harvesting. The restraint indicates a state-sponsored intelligence operation prioritizing access to policy deliberations over mass data theft.
TA419 directed phishing messages toward personnel at think tanks, universities, law firms, and defense companies. The campaign reflected consistent targeting patterns across US and Japanese institutions, emphasizing TA419’s interest in policy formulation processes rather than proprietary technology or financial data. The inclusion of an Anthropic employee as an impersonation target highlighted growing interest in AI development centers among Chinese intelligence operations.
Entities spoofed by TA419 during 2026:
| Impersonated Entity | TA419 Domain |
| Japan-Taiwan Exchange Association | tw-koryu[.]org |
| The Heritage Foundation | heritiages[.]orgheritiage[.]org |
| Shinjirō Koizumi’s Official Website(current Japanese Minister of Defense) | shinjirou[.]info |
Attribution to China derives from multiple indicators: malware analysis linked samples to known Chinese-origin tools, server infrastructure traced to Chinese networks, and targeting patterns aligned with decades of Chinese espionage priorities focused on policy development and strategic technology initiatives. Proofpoint’s threat intelligence assessed TA419 as an established actor with campaigns active since at least 2025 and expected to continue operations indefinitely.
The campaign’s success remains unclear. Proofpoint did not disclose whether attackers successfully compromised any accounts or obtained stolen emails from targets. Looks like the attackers may have achieved at least partial success against some targets. However, the narrow targeting scope and disclosure timing suggest most attempts encountered security awareness training or email filtering defenses.